Full-stack/2026
Orbit / Product workspace
A tenant-aware workspace that brings projects, access and team decisions into one clear interface.
Illustrative case study, not a claim of client work or measured production outcomes.
Concept case study. Demo and repository links are intentionally omitted; replace this content with your own verifiable project and public links.
Context
Overview
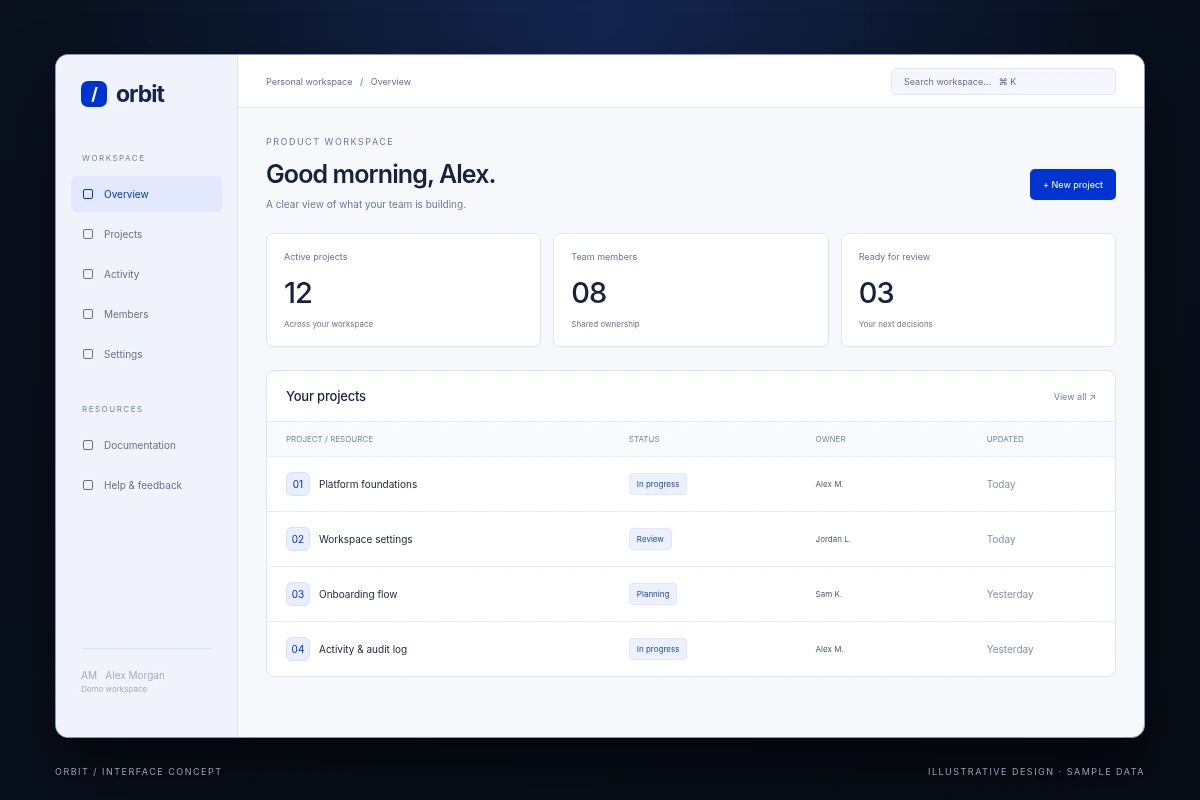
Orbit explores how a growing product team could organise projects without scattering decisions across separate tools. The concept brings workspace membership, project ownership and an activity trail into a single web application.
My focus in this illustrative project is the boundary between product experience and backend correctness: making collaboration feel straightforward without treating permissions as a client-side concern. The interface artwork uses sample data, not customer records.
The problem
A shared dashboard is easy to prototype; safe separation between organisations is not. The core problem is to support people who belong to more than one workspace while keeping project data, invitations and audit history scoped to the correct tenant.
The design also needs a clear answer to partial failure. A user should not see a successful invitation when the underlying write has failed, nor lose their work because another teammate updated the same project.
The solution
I would use a modular application with explicit tenant context, a small permission model and a transactional persistence layer. Every request resolves the active workspace on the server. Resource access is checked before a query is executed and reinforced through tenant-scoped database constraints.
On the frontend, route-level data loading, reusable form states and explicit error recovery keep the product understandable. Background work is reserved for operations that do not need to block the user, rather than introduced everywhere by default.
Ownership, made explicit
My contribution
- Application design: define the workspace, membership, project and activity domain boundaries; document which operations must be atomic.
- Backend ownership: design tenant-scoped endpoints, role checks, invitation expiry and validation errors that the UI can present without interpretation.
- Frontend implementation: build accessible workspace switching, project tables, form feedback and reusable loading/empty states.
- Data integrity: design transaction boundaries and unique constraints; add tests that attempt cross-workspace access.
- Team boundary: the visual direction and research are attributed to a hypothetical designer; this case study does not imply that I performed their work.
Architecture
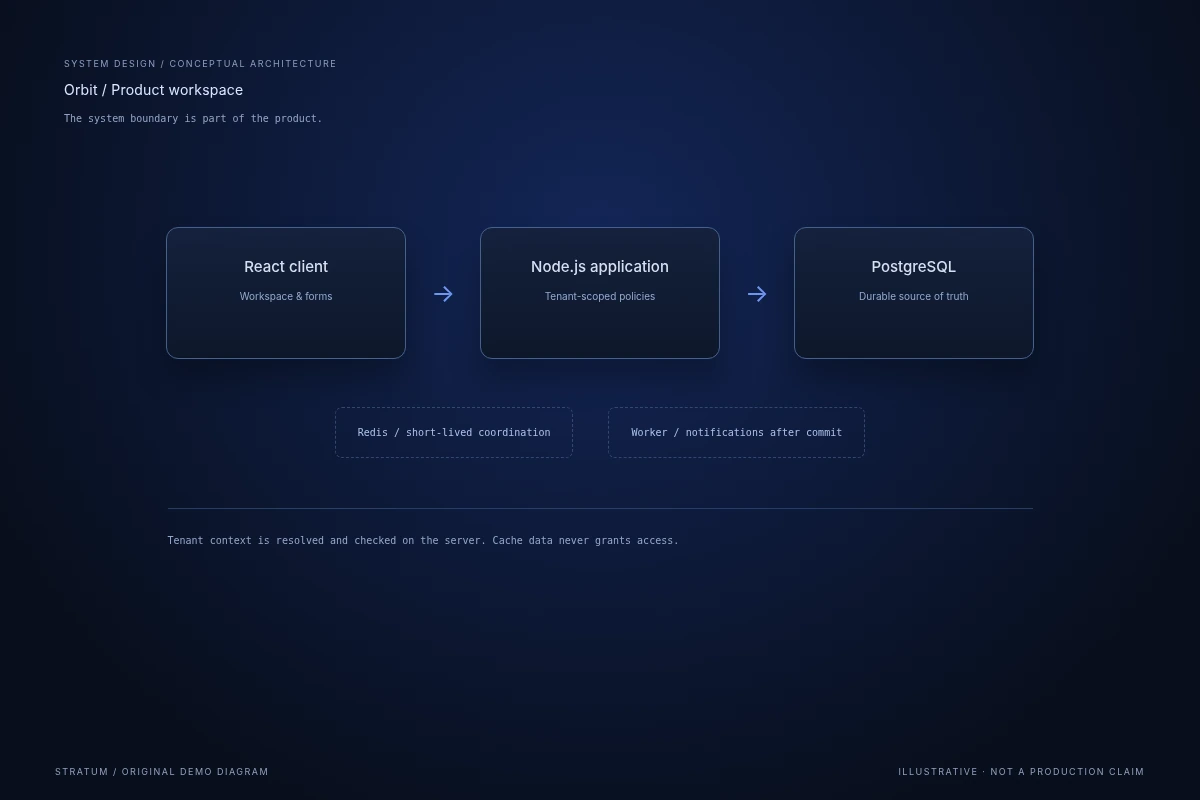
The proposed flow is React client to Node.js application to PostgreSQL. Redis is reserved for short-lived coordination and cache entries; it is not the source of truth for permissions. An asynchronous worker handles email notifications after the durable write succeeds.
A modular monolith keeps the initial deployment understandable. The membership and activity boundaries are documented so they can be separated later only when operational evidence justifies that cost.
Key features
Workspace-level permissions
Server-enforced roles with explicit access-denied states and tests for cross-tenant requests.
Project ownership
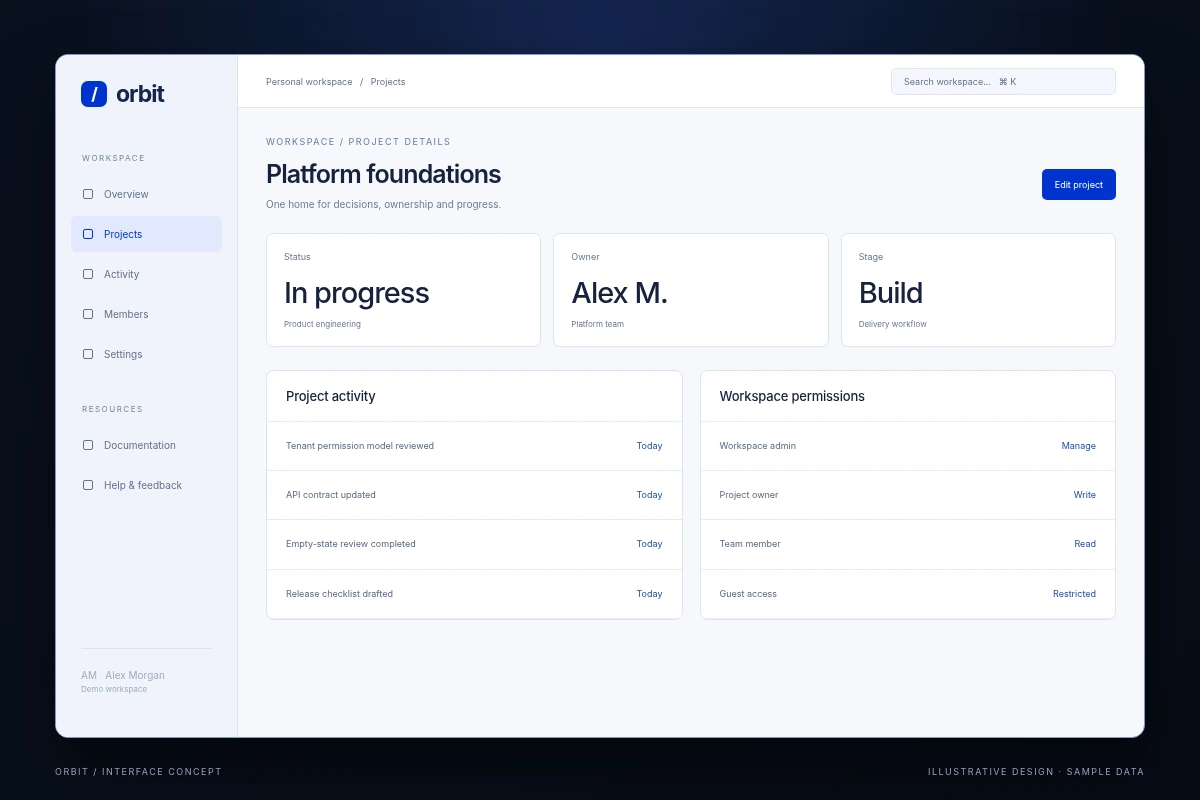
A clear owner, status and activity history on every project rather than an anonymous task grid.
Recoverable interactions
Inline validation, useful empty states and retry paths that do not silently duplicate writes.
Challenges & trade-offs
Permission checks can drift when they are repeated across controllers. A central policy layer and integration tests are more defensible than trusting a disabled UI button.
Optimistic interaction is useful for reversible changes but can mislead users during sensitive membership actions. Those operations should wait for server confirmation. Cached data must remain a convenience, not an alternative authority.
Results & impact
This concept defines a coherent product flow, a proposed permission model and a test plan for tenant isolation. It does not demonstrate a deployed customer workload.
For a real release, I would measure task completion, access-denied errors and query latency using a documented baseline. No throughput, uptime or conversion improvement is claimed here.
Screenshots
Technology stack
Application services, integrations and asynchronous workers.
DocumentationRelational modelling, transactions and query planning.
DocumentationComponent-driven interfaces and predictable client state.
DocumentationCaching, coordination and short-lived state.
DocumentationTyped application contracts and maintainable UI code.
Documentation